MDR vs EDR: Which Does Your Business Need?
EDR (Endpoint Detection and Response) is the technology that detects and lets you respond to threats on your devices. MDR (Managed Detection and Response) is a service: a provider runs EDR and other tools for you, with a 24/7 human team that monitors, investigates, and responds.
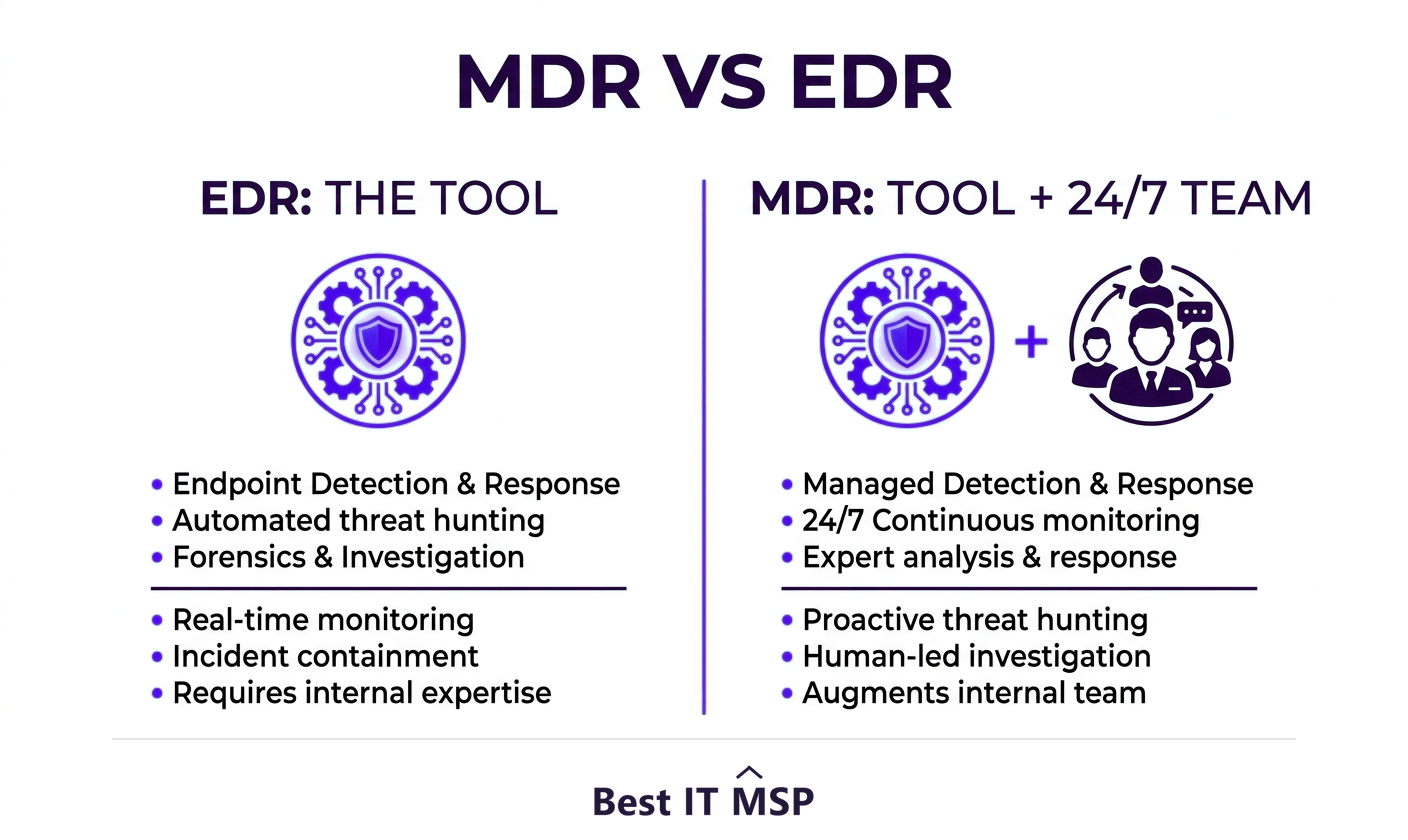
- EDR is a technology; MDR is a managed service that operates EDR (and more) for you.
- EDR detects and contains endpoint threats, but someone must monitor and act on its alerts.
- MDR adds a 24/7 security team that investigates and responds, which most SMBs lack in-house.
- Buying EDR without anyone to watch it is a common, costly mistake.
- Choose EDR if you have a security team to run it; choose MDR if you do not.
How did we compare MDR and EDR?
These two are not rival products, so a feature-by-feature scoring would mislead. The comparison is built instead around who operates the technology, which is the question that actually decides the purchase.
- What is being compared. A technology against a service, not two rival products. That asymmetry is the finding, so the comparison is framed around who operates the tool rather than which tool wins.
- The five dimensions. What it is, who operates it, coverage hours, expertise required, and scope. Each one is a question a buyer can answer about their own organisation today.
- The evidence. The load-bearing figures here are detection and staffing: how long breaches run undetected, what internal detection saves, and the size of the security hiring gap. IBM, Verizon and ISC2 are the sources, each linked where it is used.
- No vendor ranking. This compares two categories of protection. It names no products and ranks no suppliers, so nothing here is a recommendation to buy from anyone in particular.
- Independence. Best IT MSP does not sell IT services or security services, and does not appear in its own rankings.
Set out side by side, the asymmetry is easier to see than to describe.
What is the difference between MDR and EDR?
MDR and EDR are often discussed as if they were competing products to choose between, but they are not the same kind of thing at all. EDR (Endpoint Detection and Response) is a technology, a software platform that watches your laptops, desktops, and servers for suspicious behavior, detects threats, and gives you tools to investigate and respond. MDR (Managed Detection and Response) is a service, where a provider runs that technology, and usually more, on your behalf, with a team of human analysts monitoring it around the clock. Put simply, EDR is the tool; MDR is the tool plus the people who operate it.
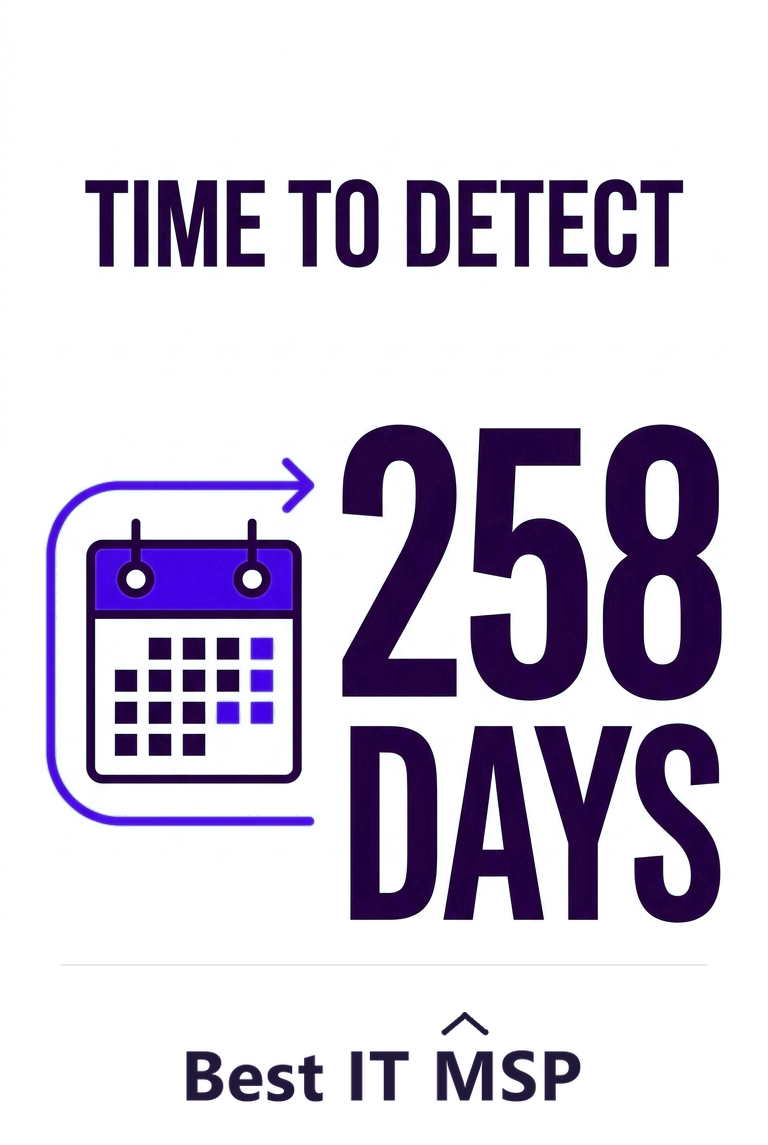
That distinction is the whole decision. Powerful detection technology only protects you if someone is watching its alerts and acting on them fast, and most small and midsize businesses have no one to do that. With the average breach taking about 258 days to identify and contain and reported cybercrime losses topping $12.5 billion in a single year, the gap between owning a tool and having it actively run is the gap between catching an attack and discovering it months too late. And since the human element features in 68 percent of breaches, the threats that slip past automated prevention are exactly the ambiguous, human-driven ones a skilled analyst is best placed to catch. This guide explains both and pairs with our managed SOC and MDR overview.
What does EDR give you?
EDR continuously monitors endpoint activity, the processes, files, and connections on each device, and uses behavioral analysis to detect threats that signature-based antivirus would miss, including ransomware and novel attacks. When it spots something, it raises an alert, records a detailed timeline of what happened, and offers response actions such as isolating the device or killing a malicious process. EDR is a genuine leap beyond traditional antivirus, and it is the modern foundation of endpoint security. What EDR does not do is decide what matters and act on it for you. It produces alerts, and alerts need a human to triage, investigate, and respond, especially the ambiguous ones that automated rules cannot resolve.
What does MDR add?
MDR wraps a fully staffed security operation around the technology. A provider deploys and tunes the EDR (and often other tools), then a team of analysts monitors it 24/7, investigates alerts, separates real threats from noise, and responds on your behalf, containing an attack at 3 a.m. without waiting for your team to wake up. Good MDR also includes proactive threat hunting and regular reporting. In effect, MDR gives a small business the security operations center (SOC) that only large enterprises could otherwise afford.
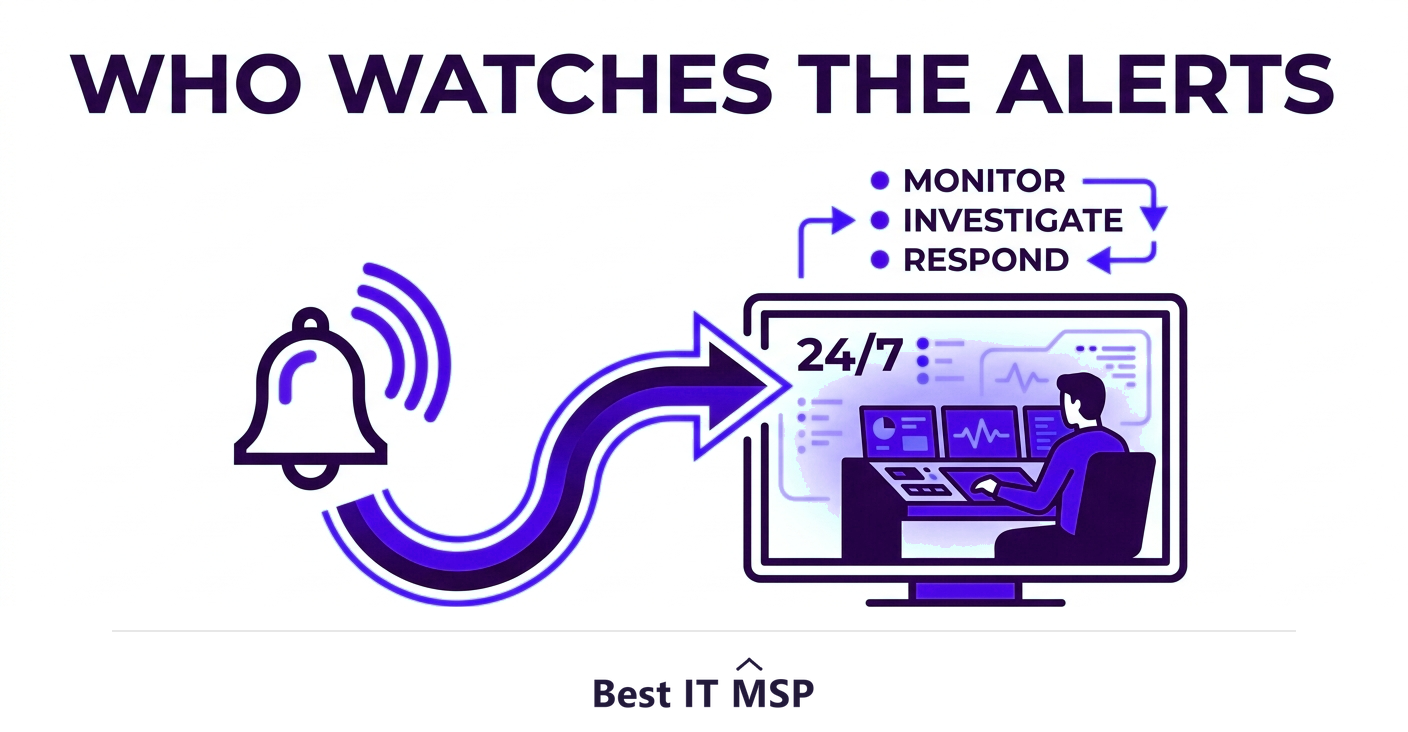
The reason MDR exists is the alert problem. Deploying EDR and leaving its alerts unwatched is one of the most common and dangerous mistakes in security, because the tool detects the attack but no one responds, and the breach proceeds anyway. MDR closes that gap with people.
How do MDR and EDR differ, dimension by dimension?
Side by side, the differences are about operation, not just capability:
| Dimension | EDR | MDR |
|---|---|---|
| What it is | Software you buy and run | A managed service you subscribe to |
| Who operates it | Your own team | The provider's team |
| Coverage hours | Detection runs continuously; response follows your staff's hours | 24/7 human monitoring and response |
| Expertise required | In-house security skills to use it well | Supplied by the provider |
| Scope | Endpoints | Often endpoints, network, cloud and identity together |
- <strong>What it is.</strong> EDR is software you buy and run; MDR is a managed service you subscribe to.
- <strong>Who operates it.</strong> With EDR, your team monitors and responds; with MDR, the provider's team does, around the clock.
- <strong>Coverage hours.</strong> EDR runs continuously, but response depends on your staff's hours; MDR provides 24/7 human monitoring and response.
- <strong>Expertise.</strong> EDR requires in-house security skills to use well; MDR brings the provider's expertise.
- <strong>Scope.</strong> EDR focuses on endpoints; MDR often correlates signals across endpoints, network, cloud, and identity.
Why do most small businesses need MDR?
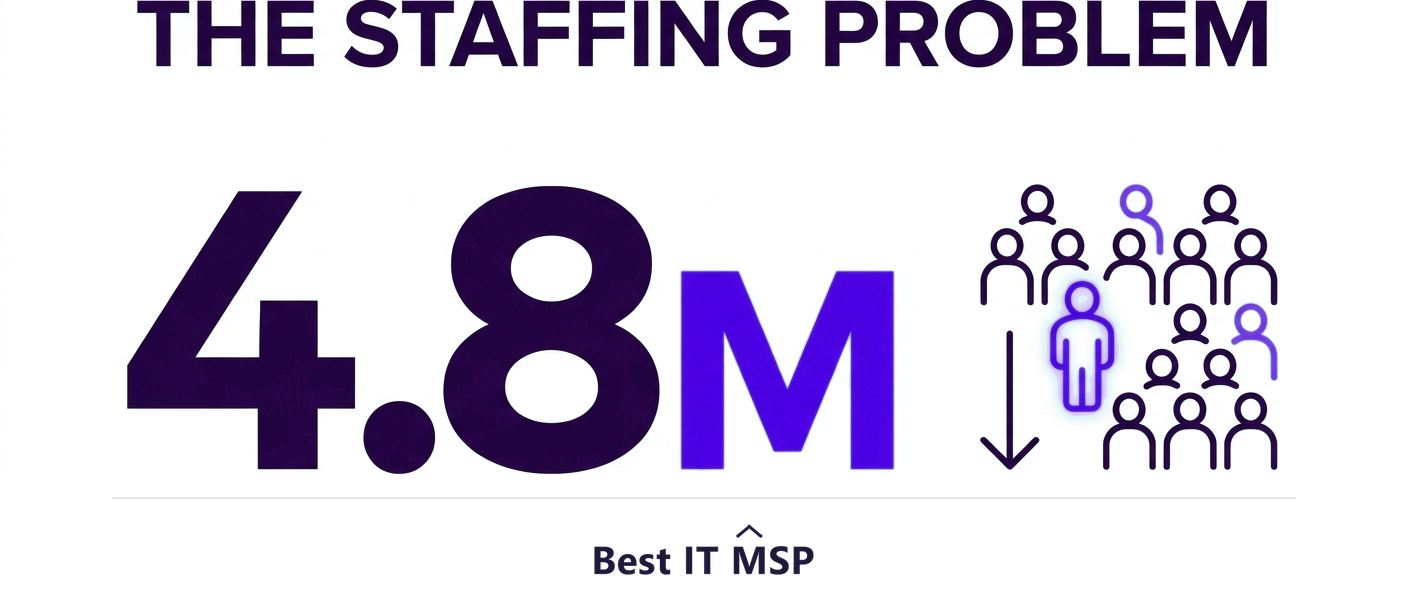
The hard truth is that buying EDR does not make you secure unless you can operate it, and operating it well means having skilled analysts available at all hours. That is exactly what most small and midsize businesses lack, and it is hard to fix by hiring, because skilled security staff are scarce amid a global shortfall of about 4.8 million cybersecurity professionals and command high salaries. Building a 24/7 internal SOC is out of reach for almost any small business. MDR solves this by spreading an expert team across many clients, so you get round-the-clock protection for a predictable fee, far less than building it yourself.
There is a measurable cost to having nobody watching. IBM reports that organisations which identified the breach with their own security teams and tools paid nearly USD 1 million less on average than those whose breach was identified by the attacker, in an extortion demand for example, and that the share detecting their own breaches rose to 42% in 2024 from 33% the year before. MDR is how a business without a security team gets into that first group.
When does EDR alone make sense?
EDR on its own is the right choice in one main case: when you already have a capable, adequately staffed internal security team that can monitor and respond to its alerts around the clock. Larger organizations with a mature SOC may run EDR themselves, sometimes alongside MDR for after-hours coverage. The deciding question is not which technology is better, it is whether you have the people to run it. If you have the team, EDR gives them a powerful tool. If you do not, EDR without MDR is a smoke detector with no one home to hear it.
Which should your business choose?
Match the choice to your security staffing. Choose EDR alone if you have a skilled internal security team that can monitor and respond 24/7. Choose MDR if you do not, which describes most small and midsize businesses, because MDR delivers both the technology and the people to make it effective. Either way, the underlying technology is similar; what differs is who runs it. Given that an hour of downtime costs most organizations more than $100,000 and the average breach costs $4.88 million, the fast, expert response MDR provides usually pays for itself by stopping incidents early. The market reflects this shift to managed security, with the managed services market projected to grow from about $330 billion in 2024 to about $879 billion over the next decade.
If you are deciding between EDR and MDR, a provider can assess your environment and staffing and recommend the right fit. To start from a vetted, merit-ranked list, browse providers by city in the Best IT MSP directory, where ranking is earned on rating and verified data.
FAQ
What is the difference between MDR and EDR?
EDR (Endpoint Detection and Response) is a technology, software that detects and lets you respond to threats on your devices. MDR (Managed Detection and Response) is a service, where a provider runs EDR and other tools for you with a 24/7 human team that monitors, investigates, and responds. EDR is the tool; MDR is the tool plus the people who operate it.
Is MDR better than EDR?
They are not directly comparable, because EDR is a technology and MDR is a service that operates that technology. MDR is better for any business that lacks a 24/7 internal security team, because powerful detection only protects you if someone monitors and acts on its alerts. For an organization with a mature security operations center, EDR alone can suffice.
Do I need MDR if I already have EDR?
If no one on your team monitors and responds to EDR alerts around the clock, then yes. Deploying EDR and leaving its alerts unwatched is a common, dangerous mistake: the tool detects the attack but no one responds, so the breach proceeds anyway. MDR provides the analysts who watch, investigate, and respond, closing that gap.
Why do small businesses choose MDR over EDR?
Because operating EDR well requires skilled security analysts available at all hours, which most small and midsize businesses lack and cannot easily hire amid a shortfall of about 4.8 million cybersecurity professionals. MDR spreads an expert 24/7 team across many clients, giving a small business enterprise-grade monitoring and response for a predictable fee.
When is EDR alone enough?
EDR alone is enough when you have a capable, adequately staffed internal security team that can monitor and respond to its alerts around the clock, typically a larger organization with a mature security operations center. The deciding question is not which technology is better but whether you have the people to operate it continuously.
Which should my business choose, MDR or EDR?
Choose EDR alone if you have a skilled internal security team that can monitor and respond 24/7. Choose MDR if you do not, which describes most small and midsize businesses, since MDR delivers both the technology and the people to make it effective. A provider can assess your staffing and environment to recommend the right fit.
Best IT MSP is the independent directory of vetted managed IT and security providers across North America. Compare merit-ranked firms in your city that deliver EDR and 24/7 MDR. No pay-to-play.